I’ve spent the last few years telling friends and family the same thing: switch to passkeys, they can’t be phished.
That advice wasn’t wrong exactly, but reading through this new research left me a little humbled. Three separate teams just showed that you don’t need to break FIDO2’s cryptography to beat it. You just need to find the messy human infrastructure sitting around it, a logging service that kept too much, a memory buffer that lingered too long, a session that trusted too easily. None of them cracked the math. All three still got in.
What The Research Actually Found
Three independent research efforts, all surfacing within the same week, demonstrated that passkey-based multi-factor authentication can be undermined without ever touching the underlying public-key cryptography that makes FIDO2 secure in the first place. The methods differ, but the throughline is the same: attackers don’t need to solve an unsolvable math problem when the systems around that math have weaker points to exploit.
The first path came from SpecterOps, which replayed Windows-exposed authentication assertions against Microsoft Entra ID. The second came from Palo Alto Networks’ Unit 42, which recovered synced passkey private keys directly out of Google Password Manager. The third came from independent researcher Dirk-jan Mollema, who showed that a Windows Hello for Business key could be used from within an already compromised session, without triggering a fresh PIN or biometric prompt. As Microsoft’s own passkey authentication documentation explains, passkeys are supposed to provide “verifier impersonation resistance,” ensuring credentials only ever get released to the legitimate service that registered them. What this research shows is that resistance can still be routed around when the surrounding environment is already compromised.
The Login Windows Kept Sitting In Plain Sight
The part of this research that genuinely surprised me came from SpecterOps principal researcher Michael Grafnetter, who presented the firm’s Pass-the-Passkey findings at Black Hat USA. According to SpecterOps’ published research, Windows had been storing past YubiKey signatures in cleartext, in a location readable by authenticated unprivileged users, including, in some configurations, remote users. Chaining those exposed signatures with weaknesses in how Entra ID validated passkey assertions allowed privileged-user impersonation, even against accounts protected by policies that explicitly required phishing-resistant MFA.
I want to be precise here, because it matters: the attacker in this chain never extracted a private key from a YubiKey or any other authenticator. What they used instead was an already-generated signature that Windows had quietly retained and that Entra ID accepted when it was replayed. That’s a narrower failure than breaking FIDO2 outright, but functionally it produces exactly the outcome any defender dreads: someone else signing in as you. The issue is now tracked as CVE-2026-34348, an information-disclosure vulnerability in the Windows Event Logging Service, with Microsoft’s affected-product list spanning releases across Windows 10, Windows 11, and Windows Server.
The Master Key Behind Google’s Synced Passkeys
The second thread of this research unsettled me for a different reason, it targets something a huge number of everyday users rely on without ever thinking about it. Unit 42’s “Pass-ta-key” research focused on Google Password Manager’s synced-passkey system inside Chrome on Windows, and all three attack variants the team demonstrated started from malware already running on the victim’s machine, without needing full administrator-level access.
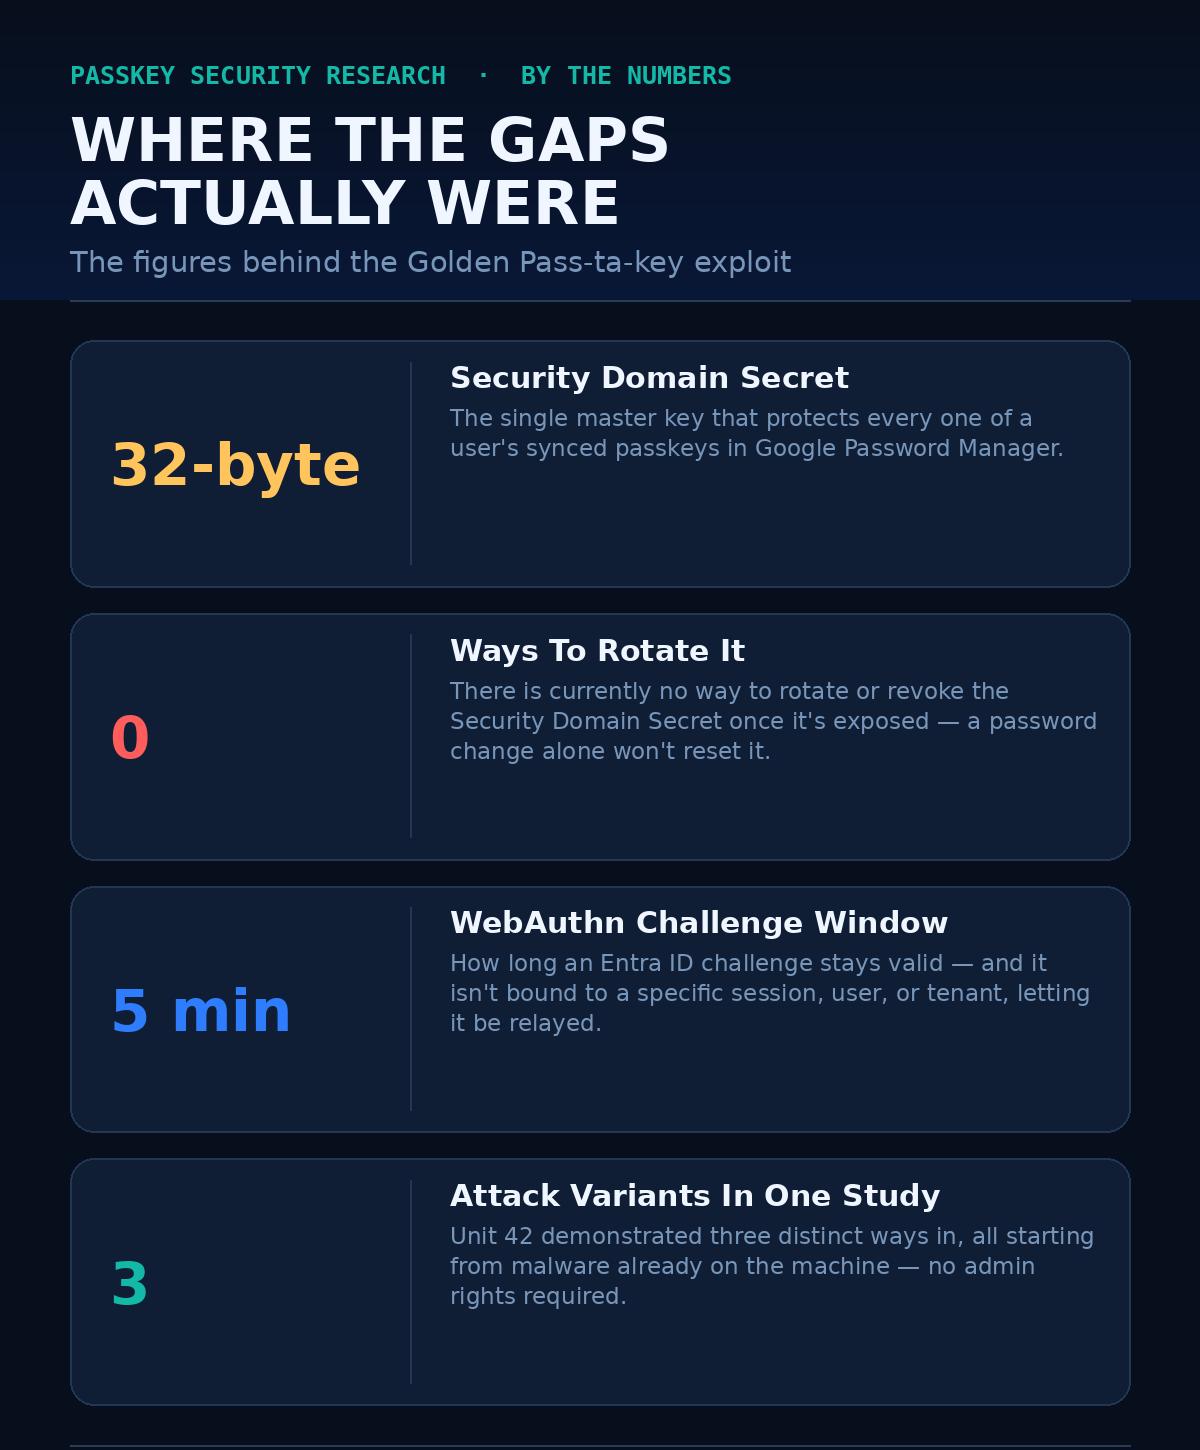
The most serious of the three, which the team calls “Golden Pass-ta-key,” goes after something called the Security Domain Secret, a 32-byte master key that protects every one of a user’s synced passkeys. Unit 42 first found this secret exposed in Chrome’s own device logging. Google has since removed it from that specific logging output, but researchers say the secret can still be temporarily present in Chrome’s process memory during re-registration. Once an attacker has it, they can recover the victim’s actual synced passkey private keys, not just replay a signature, but the key itself. What makes this genuinely alarming is persistence: currently, there’s no way to rotate or revoke that Security Domain Secret, meaning this isn’t a compromise that resets itself after a password change.
Borrowing Windows Hello Without Ever Asking For The PIN
The third piece of this puzzle, from Mollema’s Windows Hello abuse research, focuses on Windows Hello for Business. On most modern machines, its backing key sits inside the Trusted Platform Module and genuinely cannot be exported, that part of the security model holds. But Mollema found that software already running inside a victim’s compromised session doesn’t need to export the key at all. It can simply call Windows’ own cryptographic interfaces and use the key directly, without generating a new PIN or biometric prompt the user would notice.
He then took that key and used it as a valid FIDO2 credential against Microsoft Entra ID. In the process, he discovered that Entra’s WebAuthn challenge stays valid for a full five minutes and isn’t bound to a specific session, user, or tenant, meaning a challenge requested on an attacker’s system can be carried over to the victim’s machine, signed there, and returned as if nothing was wrong. The resulting sign-in can satisfy Conditional Access rules that specifically require phishing-resistant authentication, which is precisely the protection organizations deploy passkeys to enforce in the first place.
How Microsoft Has Responded So Far
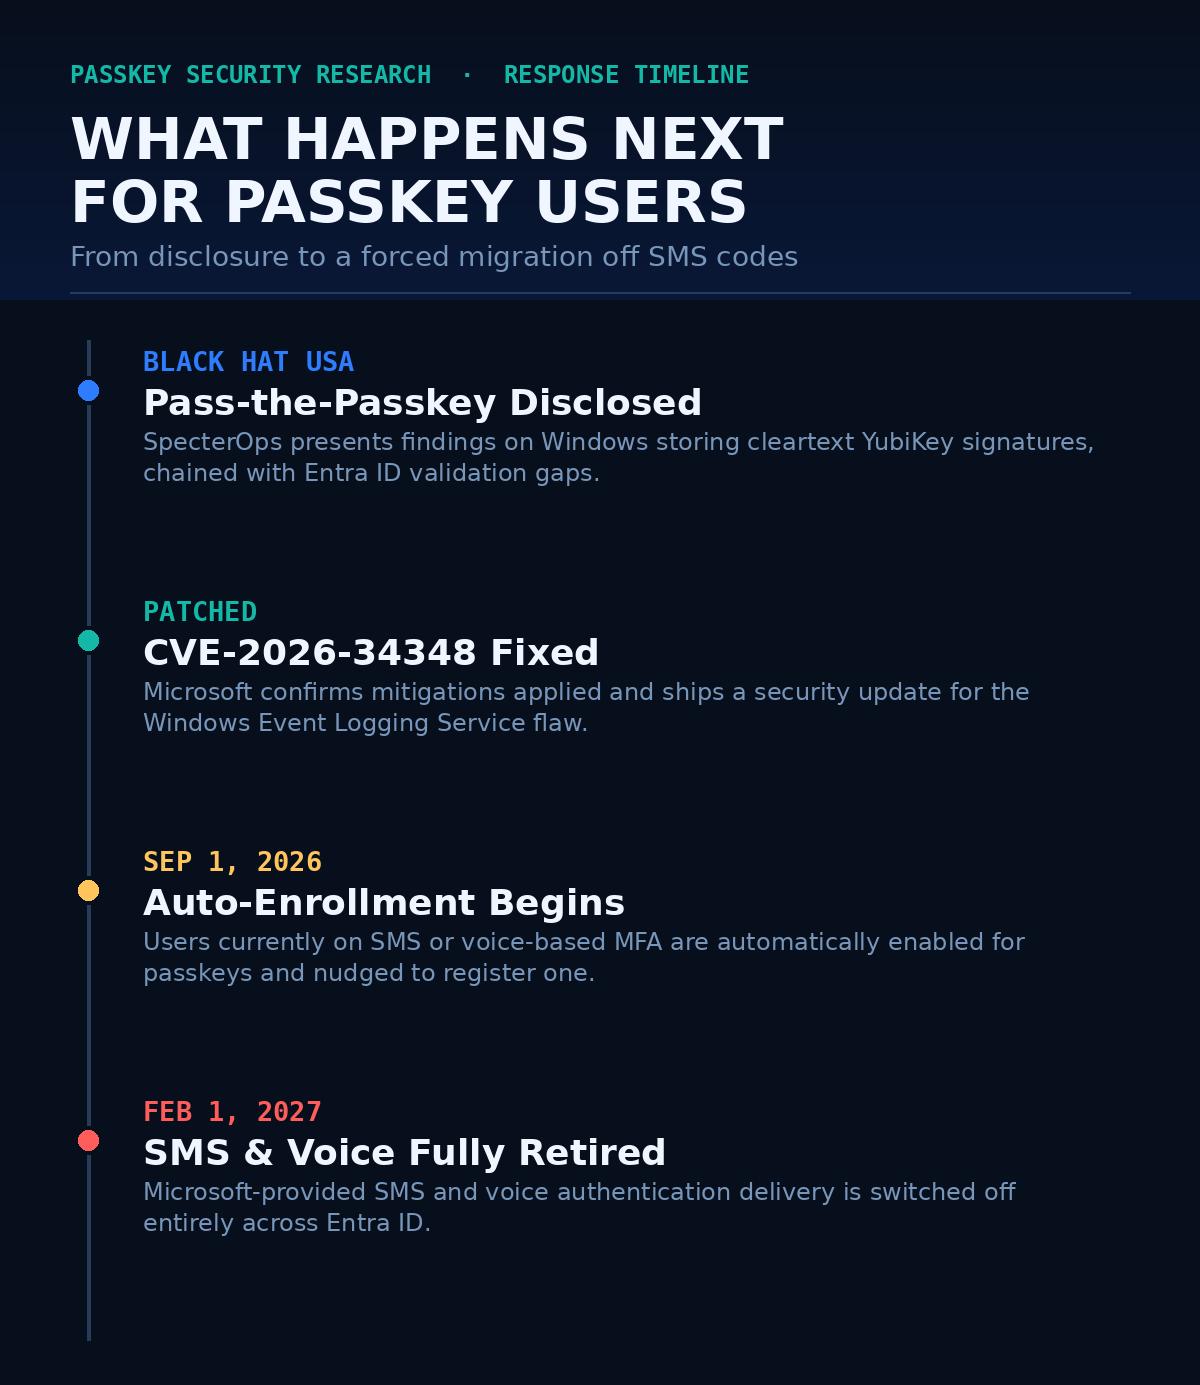
To its credit, Microsoft didn’t dismiss any of this. A company spokesperson confirmed that mitigations have already been applied for the reported issue involving passkey relay assertions, and a security update now addresses CVE-2026-34348 directly. Microsoft’s guidance continues to recommend a least-privilege access approach alongside phishing-resistant authentication and a broader Zero Trust security model as the practical countermeasure, essentially acknowledging that no single credential type, on its own, closes every gap in the surrounding system.
There’s also a timing wrinkle worth knowing about if your organization relies on Entra ID. Starting September 1, 2026, users currently enrolled in SMS or voice-based authentication will be automatically enabled for passkeys and nudged toward registering them, according to Microsoft’s own SMS and voice retirement guidance, with Microsoft-provided SMS and voice delivery fully retiring by February 1, 2027. That push toward passkeys is coming regardless of this research, which makes understanding these gaps now, rather than later, genuinely worth your time.
What This Actually Means For Anyone Using Passkeys
Here’s where I landed after sitting with all three findings: none of this means passkeys are broken, and I don’t think anyone should read it that way. FIDO2’s core cryptography is held in every single case. What failed was everything sitting around it, a logging service that retained too much, a browser that held a master secret in memory a moment too long, a validation check that didn’t bind a challenge tightly enough to the right session. Two of the three attack paths also require the attacker to already have malware or a compromised session on the victim’s machine first, meaning this isn’t a way to defeat passkeys from some anonymous position on the internet, it’s a way to make endpoint compromise go further than it should.
That distinction matters, but it doesn’t make this any less urgent to act on. If you’re running Windows in an enterprise environment, installing Microsoft’s update for CVE-2026-34348 isn’t optional at this point. If your organization accepts WebAuthn assertions, enforcing the user-verification requirements you actually request rather than just requesting them, closes a door several of these attacks walked straight through. And broadly, treating passkey stores, recovery flows, and browser memory as sensitive credential territory, the same way you’d treat a password vault, seems like the real lesson buried in all three of these findings.
Disclosure: This is not trading or investment advice. Always do your research before buying any cryptocurrency or investing in any services.
Follow us on Twitter @themerklehash to stay updated with the latest Crypto, NFT, AI, Cybersecurity, and Metaverse news!